Solutions · Security teams
Fix what actually moves exposure.
Scanner findings, control gaps and the risk register usually live in separate lists. Venevor puts them on the same records, so the first fix is the one that matters most.
- 0–1,000
- Exposure Score
- KEV + EPSS
- prioritization
1Vulnerabilities
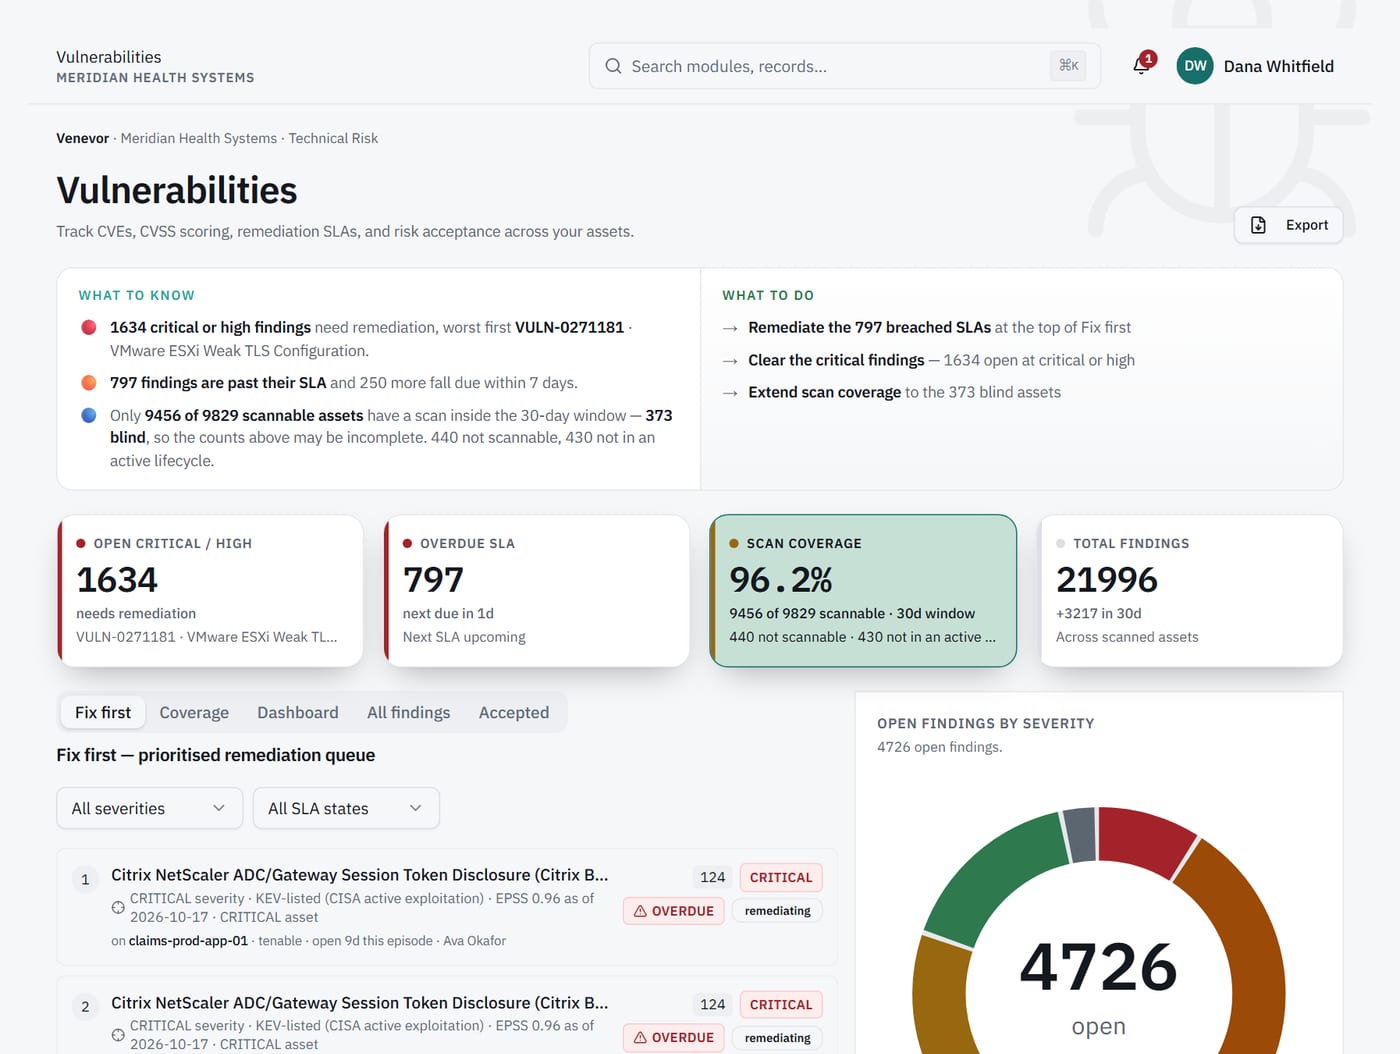
Rank findings by what attackers are using now.
Findings from Tenable and Qualys are prioritized with CISA KEV and EPSS. A fix-first queue puts known-exploited issues at the top.
What it does
Show where scanner coverage is missing.
What it never does
Treat an unreadable source as a clean result.
2Exposure
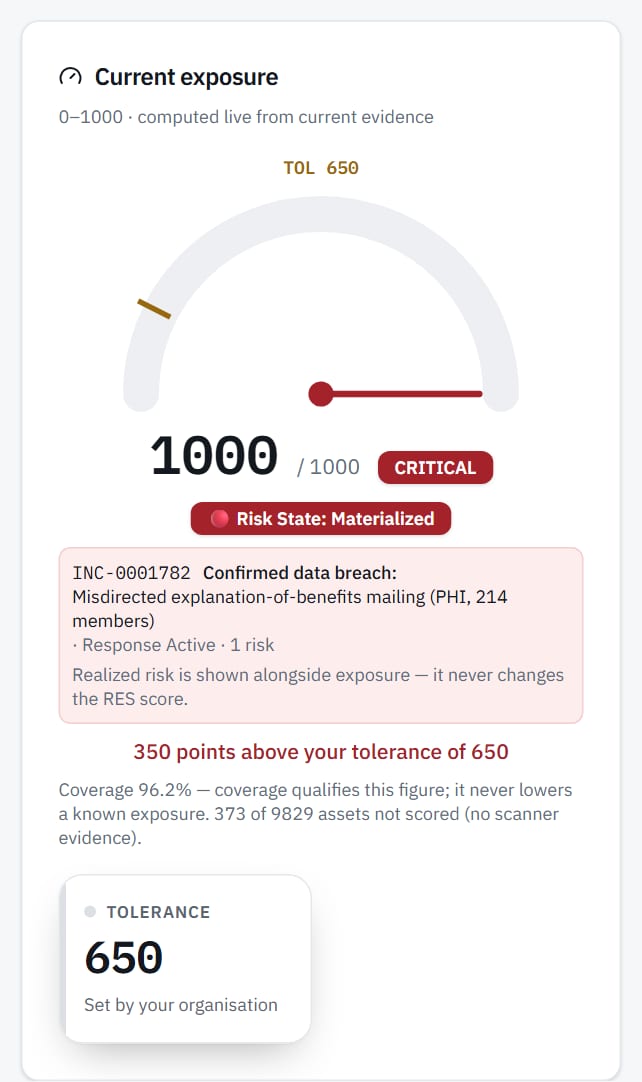
One score from asset to enterprise.
The Exposure Score runs from 0 to 1,000 at asset, business-entity and enterprise level, with daily history. Tolerance is proposed and then approved, so the line it is measured against has an owner.
3Incidents
Run incidents through phases on the record.
Incidents move through defined phases, with breach-notification status kept on the record. The ServiceNow connector brings incidents in from the service desk.
Capabilities
What's included.
Multi-source asset reconciliation
Assets reported by more than one connected source reconcile into a single record.
Endpoint and identity reads
Checks read CrowdStrike, Defender, Intune, Okta and Microsoft Entra ID.
Scanner coverage
See which assets your vulnerability scanners reach and which they miss.
Automated control checks
Security settings are checked against live systems, and one check can count toward many frameworks.
Exceptions with an expiry
An accepted gap carries a named owner and an expiry date, so it comes back for review.
Ask Venevor with citations
Ask questions about your records and get answers that cite their source.
Works with
Connected to the rest of Venevor.
FAQ
Common questions.
Which scanners does Venevor read?
Tenable and Qualys, with AWS Security Hub through the AWS connector. CISA KEV and EPSS feeds drive prioritization.
What is the Exposure Score?
A score from 0 to 1,000 at asset, business-entity and enterprise level, with daily history. Tolerance is set through a propose-and-approve step.
Does Venevor replace our scanner or EDR?
No. It reads from them and brings their results together with your assets, controls and risks, so you can decide what to fix first.
See the fix-first queue on synthetic data.
We'll walk through vulnerabilities, assets and exposure on data shaped like your estate.