Solutions · Defense contractors
Know which CMMC practices you can prove today.
Contractors preparing for CMMC work against NIST SP 800-171. Venevor shows which practices have current evidence behind them, which rest on attestation, and what to fix before the assessment.
- CMMCpractices mapped
- OSCALassessment-results export
- POA&Mfoundation export
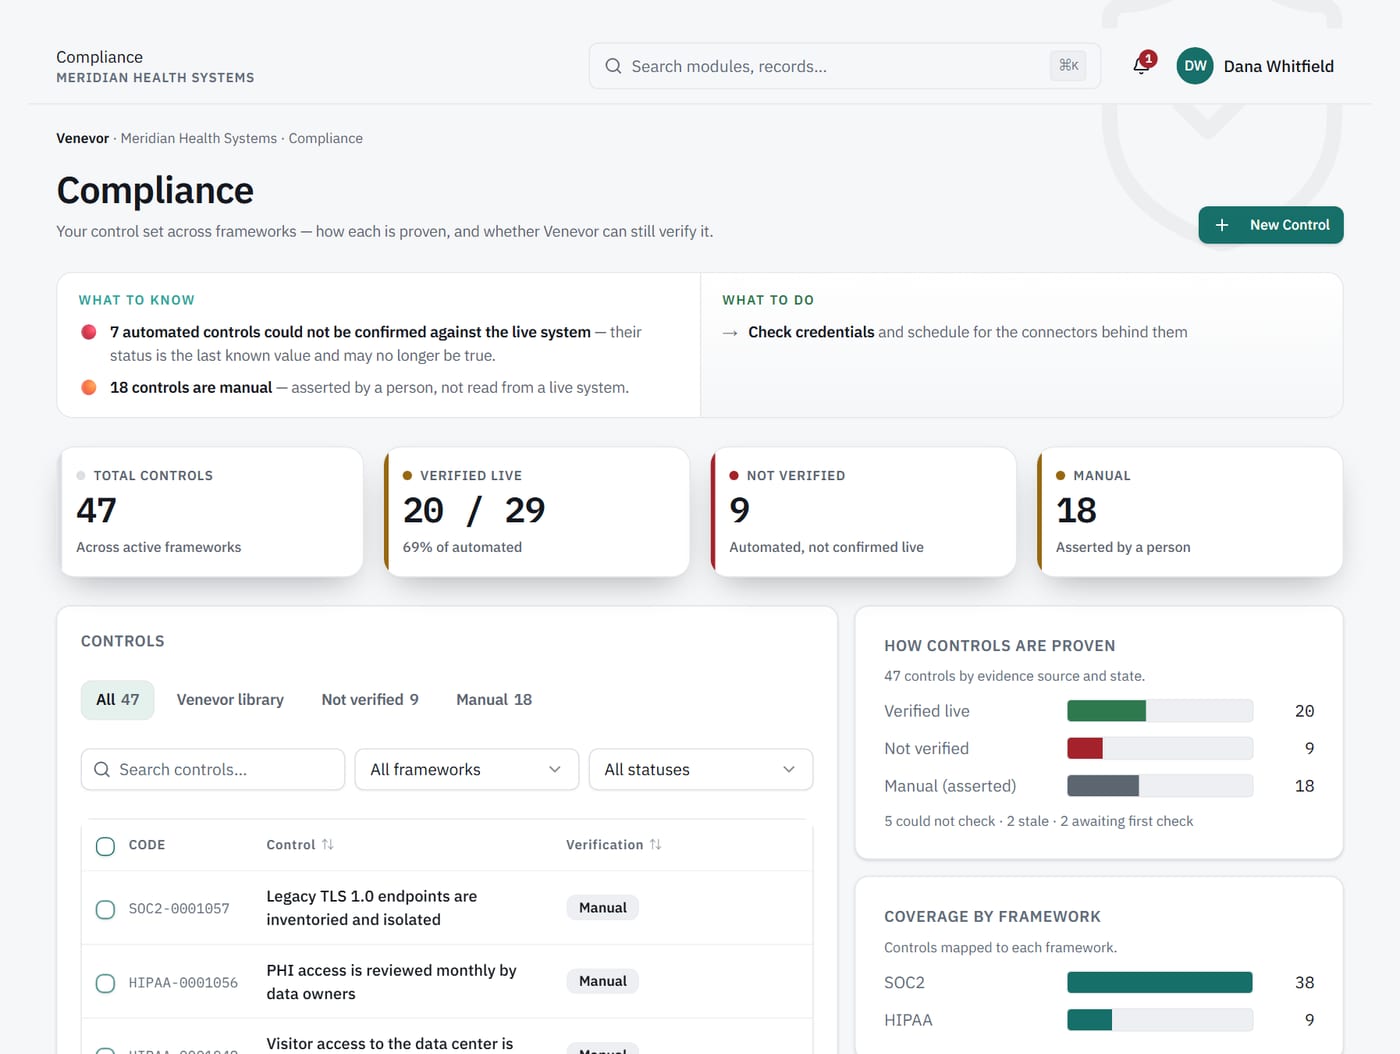
1Practices
Separate what is verified from what is attested.
Automated controls take their status from the latest check against your systems. Manual controls are marked as asserted, so an assessor can see which claims rest on a system reading and which rest on a person.
What it does
Record an unreadable source as an error.
What it never does
Count an asserted practice as verified.
2Assessment
Give assessors a dedicated workspace with live evidence.
Assessors work in a dedicated workspace that shows each control's evidence and how fresh it is. They export findings and a live evidence package without anyone assembling screenshots.
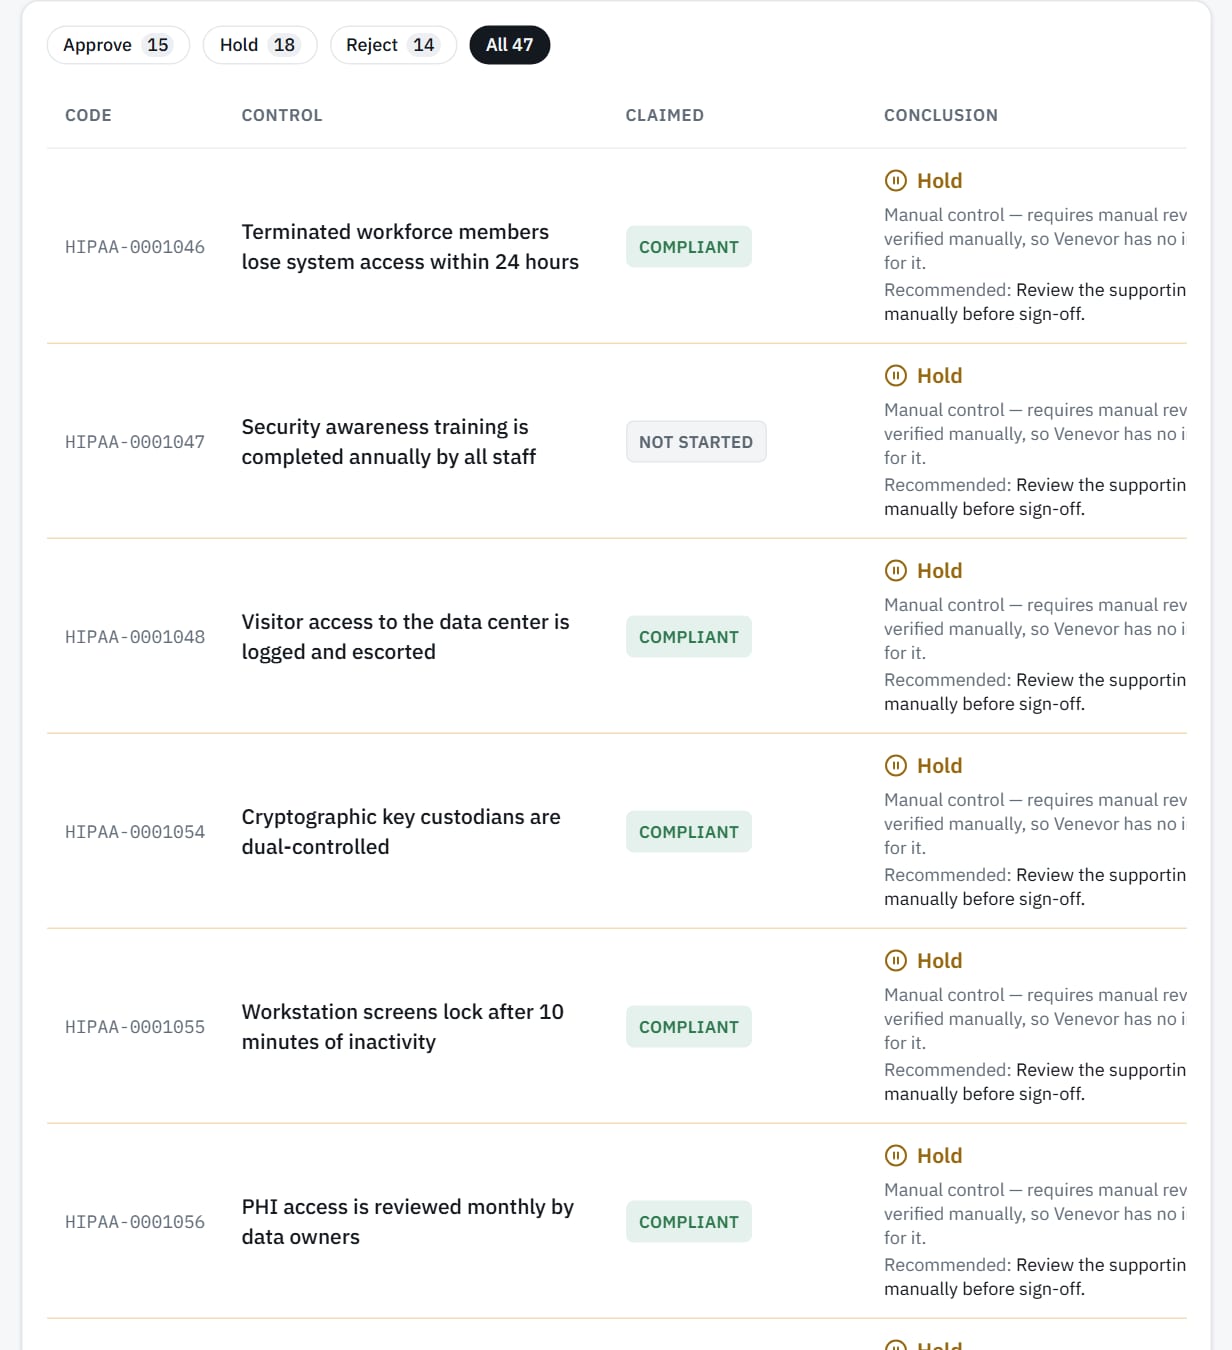
3Documentation
Export machine-readable results and POA&M foundations.
Assessment results export as OSCAL. FedRAMP SSP and POA&M foundation exports give your documentation a starting point drawn from the same records.
Capabilities
What's included.
One check, many frameworks
A single check maps to CMMC, NIST SP 800-171 and any other framework that asks for the same control.
Microsoft estate connectors
Checks read Microsoft Entra ID, Intune and Defender alongside AWS, Okta and CrowdStrike.
Fix-first vulnerability queue
Tenable and Qualys findings are ranked with CISA KEV and EPSS, so known-exploited issues come first.
Exceptions with owners
Every accepted gap has a named owner and an expiry date.
Evidence that never changes
Evidence is timestamped, kept and never edited, so a past result reads the same at assessment time.
Step-up for sensitive actions
Sensitive actions ask the user to re-authenticate, on top of mandatory multi-factor sign-in.
Works with
Connected to the rest of Venevor.
FAQ
Common questions.
Does Venevor certify us for CMMC?
No. Certification comes from an authorized assessment. Venevor prepares you for it by tracking practices, gathering evidence from your systems and showing where the gaps are.
Can we work in OSCAL?
Yes. Assessment results export in OSCAL format, and you can import OSCAL content and custom frameworks as well.
What happens when a check can't read a system?
The result is recorded as an error, and the practice is not counted as verified. Unknown stays unknown until a source can prove otherwise.
See CMMC readiness on synthetic data.
We'll walk through practices, evidence and exports on data shaped like a defense contractor's.