Frameworks · Security
SOC 2
Venevor maps your controls to the SOC 2 Common Criteria, checks the automated ones against your live systems, and keeps the evidence ready for your auditor.
- Issued byAICPA
- Applies toService organizations that hold customer data
One check
Counts toward
- SOC 2Verified
- ISO 27001Verified
- NIST CSF 2.0Verified
- HIPAAVerified
The framework
What SOC 2 asks of you.
What it is
SOC 2 is an attestation report issued by an independent CPA firm on a service organization's controls. It is built on the AICPA Trust Services Criteria, which cover security, availability, processing integrity, confidentiality and privacy. A Type I report looks at control design at a point in time, and a Type II report tests how controls operated over a period, usually several months.
System and Organization Controls 2
Who needs it
- SaaS and cloud providers selling to businesses
- Service organizations asked for a SOC 2 report in security reviews
- Teams moving from a Type I to a Type II report
1Common Criteria
Built around the criteria every report includes
Venevor's SOC 2 pack covers key Common Criteria, the security criteria that apply to every SOC 2 report. Each requirement shows its readiness and the controls behind it.
2Type II
Evidence that covers the whole audit period
A Type II audit asks how controls operated over months. Automated checks run on a schedule and keep every timestamped result, so the history is there when your auditor asks for it.
What it does
Keeps every check result with its time and source, and flags evidence that has gone stale.
What it never does
Record an unreadable check as a pass. An error stays an error.
3Auditor access
Give your auditor a dedicated workspace
Your auditor sees the controls, evidence and history in scope, with export and a live evidence package for the audit. They can review everything and change nothing.
Capabilities
Built for SOC 2.
Automated control status
An automated control's status comes from its latest check, and nobody can set it by hand.
Collect evidence once
One check maps to every framework it supports, so SOC 2 evidence also counts toward ISO 27001 or NIST CSF.
Five readiness states
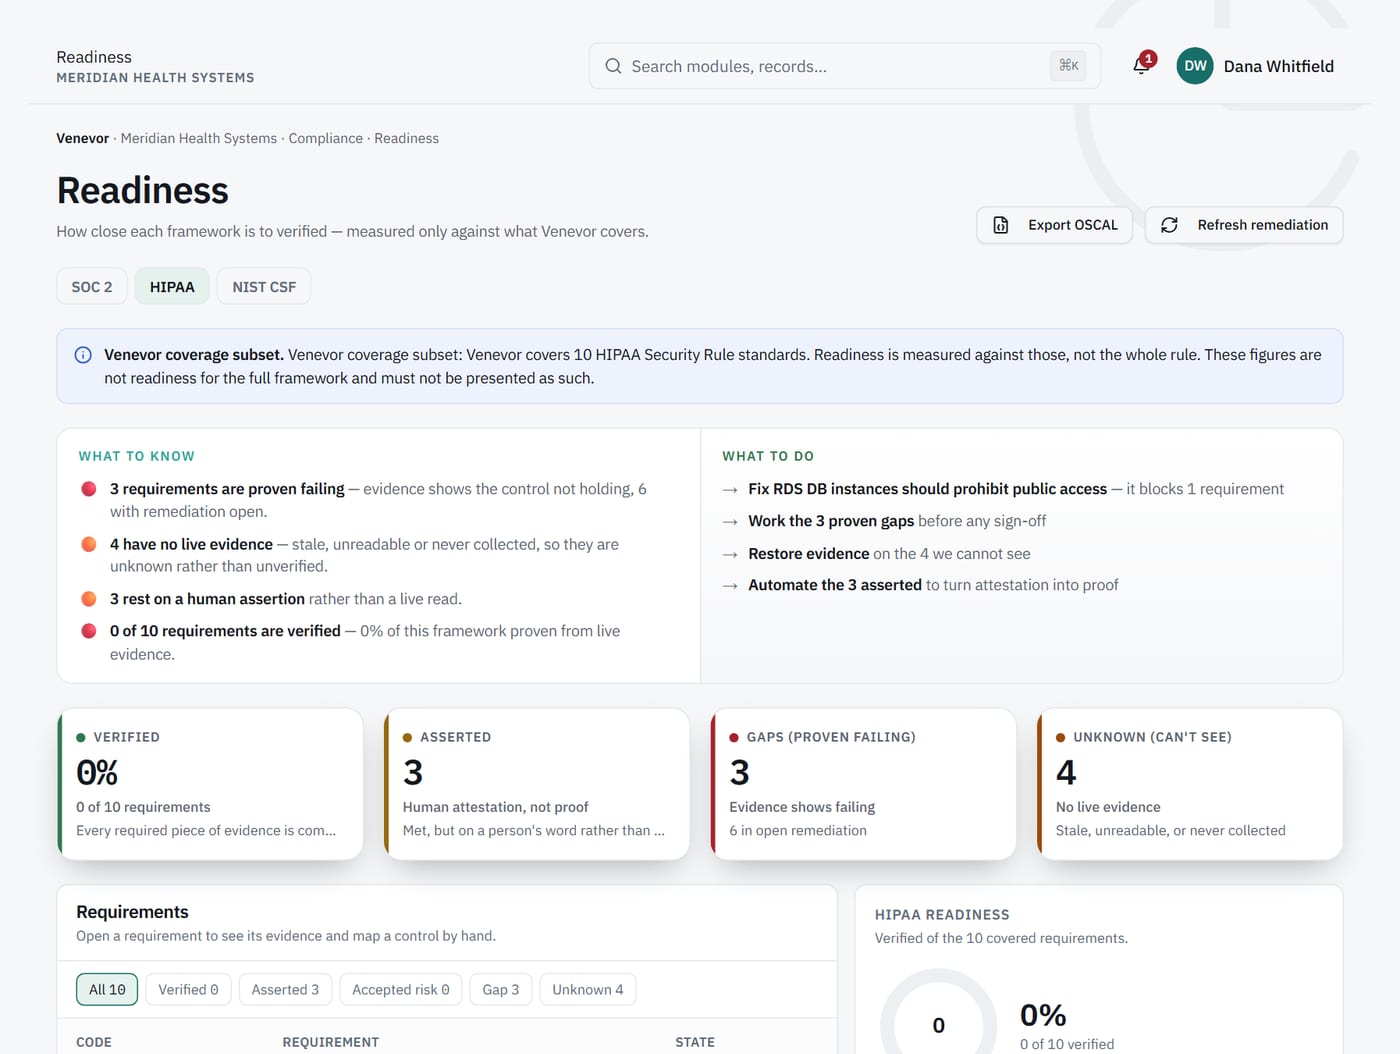
Each requirement is Verified, Asserted, Exception, Gap or Unknown, and verified and asserted are never added together.
Policy approvals
Policies are approved with e-signature and acknowledged by staff, and the record is kept.
Vendor questionnaires
Send questionnaires to vendors and keep their responses with the vendor's record.
SOC 2 readiness report
Share a readiness report that shows where you stand before fieldwork begins.
One set of evidence
The same checks count toward other frameworks.
- Security
ISO 27001
Prepare your ISMS and Annex A controls for certification.
See ISO 27001 → - Security
NIST CSF 2.0
Map your program to the six CSF 2.0 Functions.
See NIST CSF 2.0 → - Privacy
HIPAA
Track HIPAA Security Rule safeguards with live evidence.
See HIPAA → - Compliance
Compliance automation
Controls that prove themselves from live checks.
Learn more → - Compliance
Evidence
Every check result, timestamped and kept.
Learn more → - Compliance
Audits & auditor workspace
Live evidence packages and a dedicated auditor view.
Learn more →
FAQ
SOC 2 questions.
Does Venevor replace my SOC 2 auditor?
No. A SOC 2 report can only be issued by an independent CPA firm. Venevor prepares and organizes the evidence, and gives your auditor a dedicated workspace to review it.
Which trust services criteria does the SOC 2 pack cover?
Key Common Criteria, which apply to every SOC 2 report. If your scope adds availability, confidentiality, processing integrity or privacy, you can bring those requirements in as a custom framework.
Can we use Venevor for both a Type I and a Type II?
Yes. For a Type I, the readiness view shows where control design stands. For a Type II, scheduled checks keep a timestamped history of results across the audit period.
Which systems can Venevor check?
Built connectors include AWS (with Security Hub), Okta, GitHub, Microsoft Entra ID, Intune, Defender, CrowdStrike, Tenable, Qualys, ServiceNow and Jira. Controls without a connector stay manual, and their readiness is never counted as verified.
See your SOC 2 readiness on real evidence.
A walkthrough built around your frameworks and the systems you already run.