Frameworks · Financial
NYDFS 23 NYCRR 500
Venevor tracks the Part 500 requirements, checks what it can read from your systems, and keeps the dated evidence behind your annual filing.
- Issued byNew York State Department of Financial Services
- Applies toFinancial services companies licensed by NYDFS
One check
Counts toward
- NYDFS 23 NYCRR 500Verified
- NIST CSF 2.0Verified
- SOC 2Verified
- ISO 27001Verified
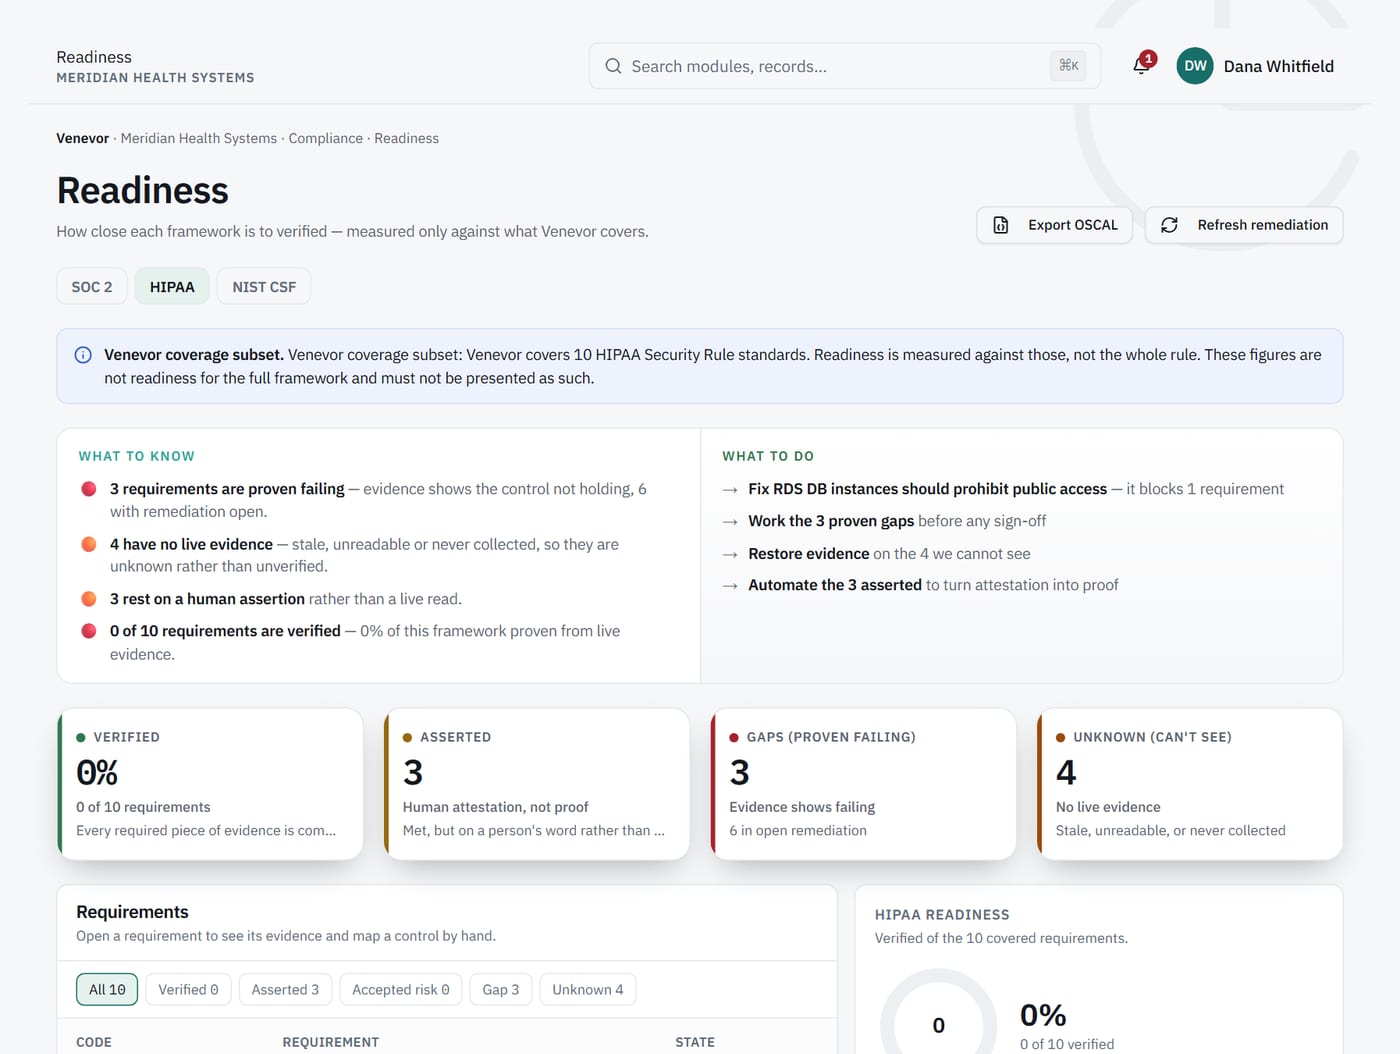
The framework
What NYDFS 23 NYCRR 500 asks of you.
What it is
23 NYCRR 500 is the cybersecurity regulation the New York State Department of Financial Services applies to the banks, insurers and other financial services companies it licenses. It requires a risk-based cybersecurity program, a CISO, written policies, multi-factor authentication, an asset inventory and notice to the Department of certain cybersecurity events. Each year, covered entities file either a certification of compliance or an acknowledgment of noncompliance.
23 NYCRR Part 500, Cybersecurity Requirements for Financial Services Companies
Who needs it
- Banks, insurers and money transmitters licensed in New York
- Larger Class A companies with added requirements
- Financial services firms preparing their annual filing
1Annual filing
Evidence behind your annual certification
Each year your organization certifies compliance or acknowledges where it falls short. Venevor keeps the timestamped evidence and readiness history behind that decision, and the filing itself stays with you.
2Access and assets
MFA and asset inventory read from source systems
Identity connectors such as Okta and Microsoft Entra ID, and device connectors such as Intune, read the systems your access and inventory requirements depend on.
What it does
Takes an automated control's status from its latest check.
What it never does
Let anyone set that status by hand.
3Board oversight
Reporting for your senior governing body
Part 500 expects the board to oversee the cybersecurity program. Venevor's board report gives them a current view of readiness, with verified and asserted kept separate.
Capabilities
Built for NYDFS 23 NYCRR 500.
Part 500 pack
Program, governance, access, inventory and incident requirements, mapped to your controls.
Incident tracking
Incidents record their breach-notification status, so notice decisions are documented.
Asset inventory
Assets come in from connected systems such as Intune and ServiceNow.
Third-party questionnaires
Assess third-party service providers with questionnaires and keep their responses.
Exceptions with expiry
Every exception has an owner and an expiry date, and it never overrides an automated status.
Board report
Give the board a current view of readiness built from live evidence.
One set of evidence
The same checks count toward other frameworks.
- Security
NIST CSF 2.0
Map your program to the six CSF 2.0 Functions.
See NIST CSF 2.0 → - Security
SOC 2
Prepare Common Criteria evidence for your SOC 2 audit.
See SOC 2 → - Security
ISO 27001
Prepare your ISMS and Annex A controls for certification.
See ISO 27001 → - Compliance
Compliance automation
Controls that prove themselves from live checks.
Learn more → - Operations
Incident management
Incidents tracked by phase, with breach notification.
Learn more → - Operations
Third-party risk
Vendor questionnaires, portal and approval routing.
Learn more →
FAQ
NYDFS 23 NYCRR 500 questions.
Does Venevor file our annual certification?
No. Your organization files the certification or acknowledgment with NYDFS. Venevor keeps the evidence and readiness history your signers review before they file.
Can Venevor help with cybersecurity event notices?
Incidents in Venevor record a breach-notification status, so the notice decision is documented with the incident. Determining whether to notify, and sending the notice, stay with your organization.
How do we handle third-party service providers?
Send vendor questionnaires, keep the responses with each vendor's record, and track third-party risk beside your own controls.
Can examiners or auditors review our evidence?
Yes. Give them a dedicated workspace with the controls, evidence and history in scope, with export.
See your NYDFS 23 NYCRR 500 readiness on real evidence.
A walkthrough built around your frameworks and the systems you already run.