Frameworks · Security
NIST CSF 2.0
Venevor maps your controls to the NIST CSF 2.0 outcomes, checks the ones it can read from your systems, and shows leadership where the program stands.
- Issued byNIST
- Applies toOrganizations of any size or sector
One check
Counts toward
- NIST CSF 2.0Verified
- NIST SP 800-171Verified
- ISO 27001Verified
- HIPAAVerified
The framework
What NIST CSF 2.0 asks of you.
What it is
The NIST Cybersecurity Framework is voluntary guidance for managing cybersecurity risk, written as a set of outcomes that each organization chooses how to achieve. Version 2.0, released in 2024, organizes those outcomes into six Functions: Govern, Identify, Protect, Detect, Respond and Recover. Govern is new in 2.0, and the framework's scope now covers organizations of every kind, beyond critical infrastructure.
NIST Cybersecurity Framework 2.0
Who needs it
- Security leaders building or measuring a program
- Organizations reporting cybersecurity posture to a board
- Teams using CSF as a common language across other frameworks
1Six Functions
Govern through Recover in one view
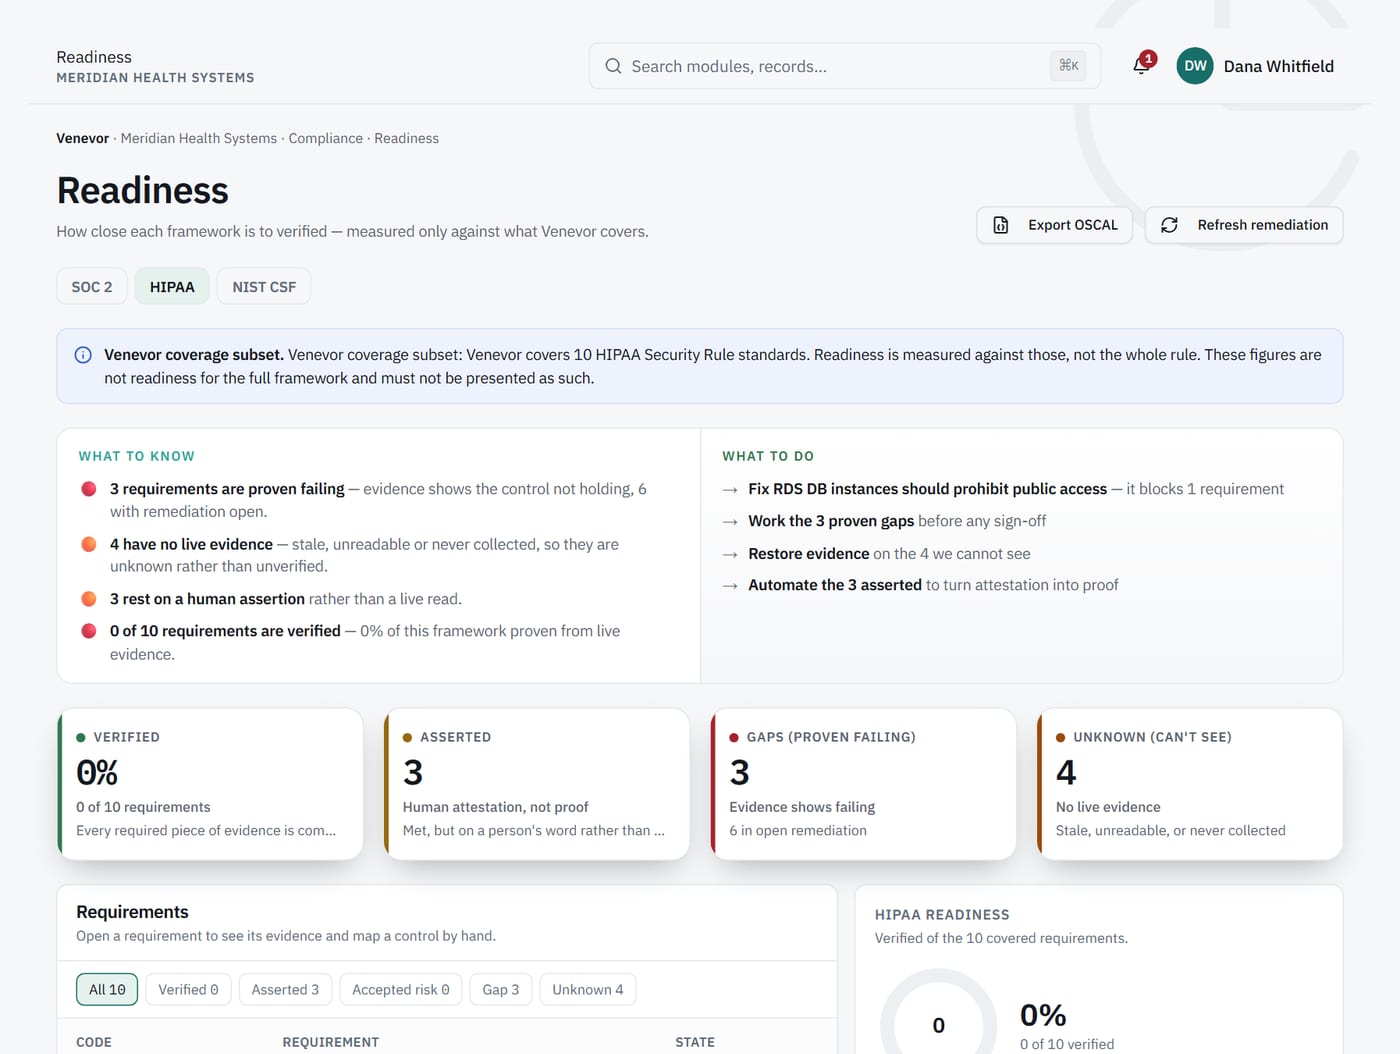
Each CSF outcome shows its readiness, so you can see which are verified, which are asserted and which are still a gap across all six Functions.
2Govern
Board reporting from the same evidence
The Govern Function puts cybersecurity in front of leadership. Venevor's board report draws on the same readiness data your team works from.
3Crosswalk
One control, many frameworks
CSF often sits alongside SOC 2, HIPAA or ISO 27001. One check maps to every framework it supports, so evidence is collected once.
What it does
Keeps verified and asserted separate in every total.
What it never does
Show an outcome nobody can check as fine. It shows as Unknown.
Capabilities
Built for NIST CSF 2.0.
CSF 2.0 pack
Outcomes across all six Functions, mapped to your controls.
Five readiness states
Verified, Asserted, Exception, Gap and Unknown, with verified and asserted never added together.
Framework overlap view
See where CSF shares controls with your other frameworks.
Board report
Give leadership a current view of readiness built from live evidence.
Risk register
Record risks with owners and treatment, linked to related controls.
Live connectors
AWS, Okta, GitHub, Microsoft Entra ID and other connectors supply evidence directly.
One set of evidence
The same checks count toward other frameworks.
- Government
NIST SP 800-171
Rev. 2 and Rev. 3 packs for protecting CUI.
See NIST SP 800-171 → - Security
ISO 27001
Prepare your ISMS and Annex A controls for certification.
See ISO 27001 → - Privacy
HIPAA
Track HIPAA Security Rule safeguards with live evidence.
See HIPAA → - Compliance
Compliance automation
Controls that prove themselves from live checks.
Learn more → - Risk
Enterprise risk
A risk register scored, treated and tied to controls.
Learn more → - Insight
Reports & dashboards
Built-in and custom reports, scheduled and exported.
Learn more →
FAQ
NIST CSF 2.0 questions.
Can we be certified against NIST CSF?
No. NIST CSF is voluntary guidance with no certification program. Many organizations use it to measure and report on their program, and Venevor helps track progress against its outcomes.
We used CSF 1.1. Does Venevor support 2.0?
Yes. Venevor's pack is built on CSF 2.0, including the new Govern Function.
Can we use CSF alongside other frameworks?
Yes. One check maps to every framework it supports, and the overlap view shows where CSF shares controls with SOC 2, HIPAA, ISO 27001 and others.
Who decides which outcomes apply to us?
You do. CSF expects each organization to choose its outcomes based on its own risk. Venevor records the controls and evidence behind those choices, and an exception with an owner and expiry covers anything you accept for now.
See your NIST CSF 2.0 readiness on real evidence.
A walkthrough built around your frameworks and the systems you already run.