Frameworks · Government
CMMC
Venevor gives you a profile for the CMMC level you are targeting, maps it to the NIST SP 800-171 practices behind it, and keeps the evidence an assessor will ask for.
- Issued byU.S. Department of Defense
- Applies toDefense contractors handling FCI or CUI
One check
Counts toward
- CMMCVerified
- NIST SP 800-171Verified
- NIST CSF 2.0Verified
The framework
What CMMC asks of you.
What it is
CMMC is the Department of Defense program for verifying that contractors protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). It has three levels: Level 1 covers basic safeguarding of FCI, Level 2 aligns with NIST SP 800-171, and Level 3 adds selected requirements from NIST SP 800-172. Depending on the level and the contract, the assessment is a self-assessment, a third-party assessment by a C3PAO, or a government-led assessment.
Cybersecurity Maturity Model Certification
Who needs it
- Prime contractors and subcontractors in the defense industrial base
- Organizations that store or process CUI
- Suppliers preparing for a C3PAO assessment
1Levels
A profile for the level you need
Venevor has profiles for CMMC Levels 1, 2 and 3. Pick the one your contracts require, and readiness is measured against that level's practices.
2NIST SP 800-171
Level 2 practices mapped to NIST SP 800-171
Level 2 aligns with NIST SP 800-171, so one control can serve both. Venevor maps each check to every framework it supports, and evidence is collected once.
What it does
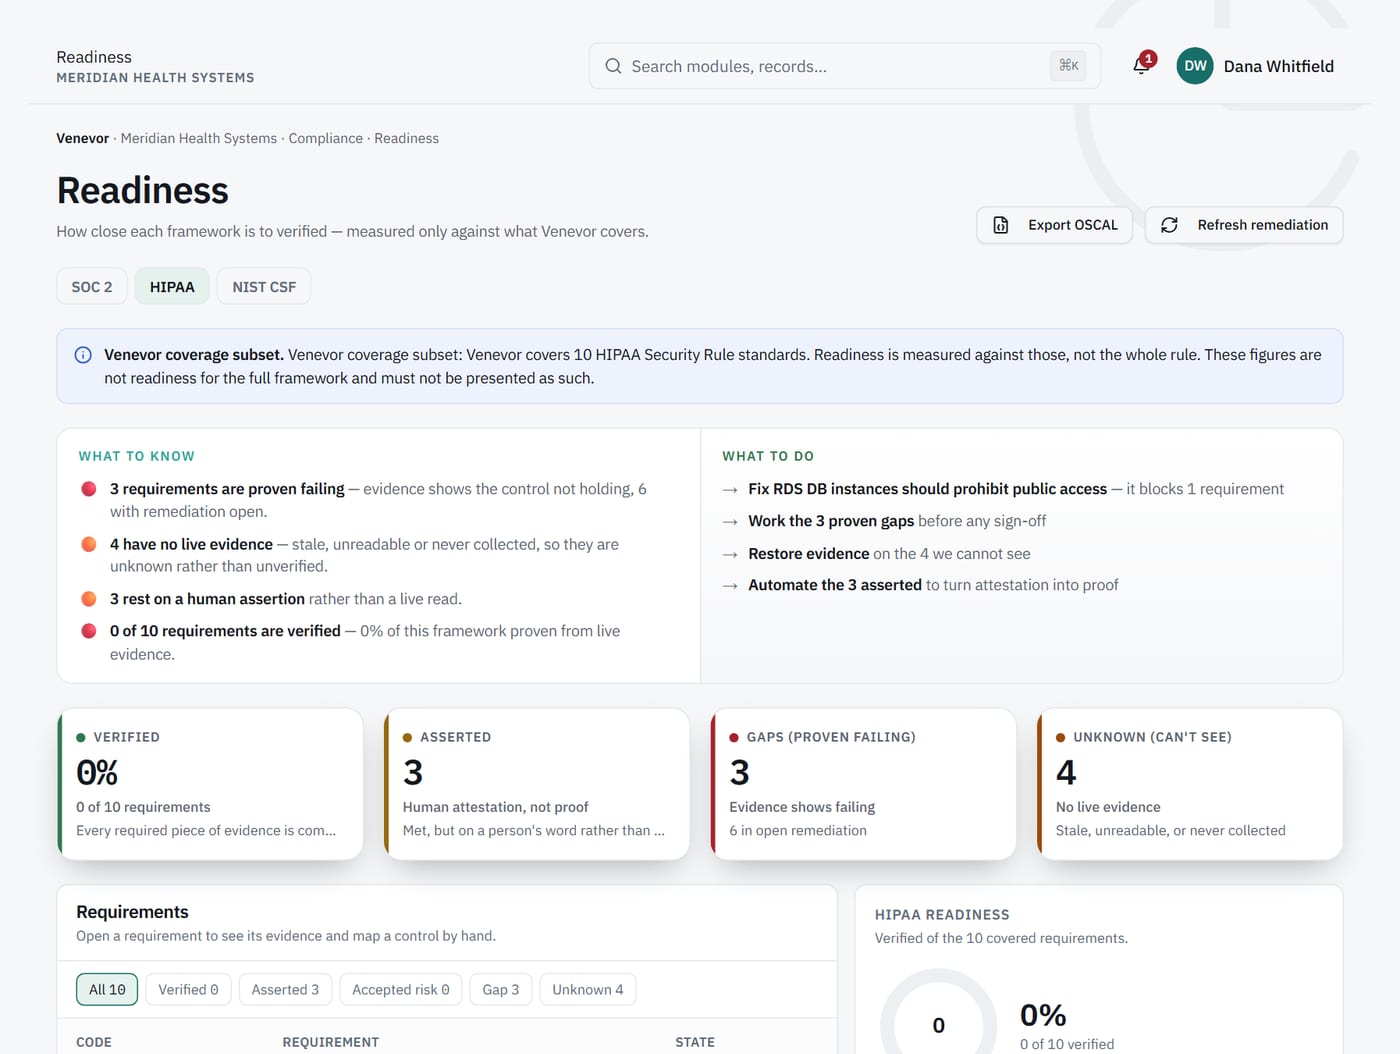
Shows which practices are verified by a live check and which rest on a person's assertion.
What it never does
Count an asserted practice as verified.
3Assessment
Ready for the assessor's questions
Assessors get a dedicated workspace with the evidence and its history. FedRAMP SSP and POA&M foundation exports give your team a structured starting point for those documents.
Capabilities
Built for CMMC.
Level 1 to 3 profiles
Measure readiness against the level your contracts require.
Crosswalk to 800-171
One check maps to CMMC and NIST SP 800-171 at the same time.
Live endpoint evidence
Connectors such as Intune, Defender and CrowdStrike read endpoint state directly.
Gaps you can act on
Requirements without evidence show as Gap or Unknown, never as fine.
Time-bound exceptions
Exceptions carry an owner and an expiry date and never change an automated status.
OSCAL export
Export assessment results in OSCAL format.
One set of evidence
The same checks count toward other frameworks.
- Government
NIST SP 800-171
Rev. 2 and Rev. 3 packs for protecting CUI.
See NIST SP 800-171 → - Security
NIST CSF 2.0
Map your program to the six CSF 2.0 Functions.
See NIST CSF 2.0 → - Compliance
Compliance automation
Controls that prove themselves from live checks.
Learn more → - Compliance
Evidence
Every check result, timestamped and kept.
Learn more → - Compliance
Audits & auditor workspace
Live evidence packages and a dedicated auditor view.
Learn more →
FAQ
CMMC questions.
Is Venevor a C3PAO?
No. Venevor is software. Level 2 certification assessments are performed by authorized C3PAOs, and Level 3 assessments by the government. Venevor helps you prepare and gives your assessor access to the evidence.
Which CMMC level should we target?
That depends on the information you handle and what your contracts require. Level 1 applies to FCI, and Levels 2 and 3 to CUI. Your contract language and contracting officer are the authority here.
Can we reuse the same work for NIST SP 800-171?
Yes. Level 2 aligns with NIST SP 800-171, and Venevor maps each check to both, so evidence is collected once.
Does Venevor produce our System Security Plan?
Venevor offers FedRAMP SSP and POA&M foundation exports. Treat them as a starting point that your team completes and reviews.
See your CMMC readiness on real evidence.
A walkthrough built around your frameworks and the systems you already run.